
Cvax
Slavan
- Učlanjen(a)
- 29.04.2022
- Poruke
- 747
- Poena
- 325

Zbog zašto?U US of A od sada kupci koji kupuju RTX 5090 moraju da popune istu dokumentaciju kao za kupovinu oružja.
Vlasnički podatci, lokacija na kojoj će biti korišćenja, obaveza da se izda obaveštenje ako se ista preproda, uz naravno zabranu izvoza i preprodaje stranim državljanima.

Кад већ згрћу толике паре, могли би да купе лиценце за имена клубова, а не да имамо Нормандију ФЦ и остале у 2026.години.


 torrentfreak.com
Daleko od istine. Osim ako pod "svuda u svetu" podrazumevaš mahom Zapad, onda da 🙂Koje cimanje sto ce fazon sacica balkanaca da skine igru za dzabe. Svuda u svetu ljudi kupuju igre, piraterija maltene i ne postoji.
Kao neko ko je ziveo u par razlicitih drzava koje nisu na istim kontinentima mogu samo da ti kazem da ne mozes da budes vise u krivu.Koje cimanje sto ce fazon sacica balkanaca da skine igru za dzabe. Svuda u svetu ljudi kupuju igre, piraterija maltene i ne postoji.

Verovatno vec postovano ali vredi da bude u ovoj temi jer ovo je verovatno jedan od najvecih potresa/preokreta u industriji u poslednjih ko zna koliko godina:
Ne znam samo zašto misle da će im ljudi plaćati 80+ evra za AI designed igre. Ja već sada kada na Steam pročitam da neka indie igra u određenom aspektu koristi AI ne želim da potrošim desetak evra, ovo ne bi plaćao uopšte nego isključivo piracy i high seas. Ne znam jel gledate malo GitHub, na CLAUDE.md projekte niko neće da potroši ni dinara, ma ni da commituju kod, kao da su šugavi.Verovatno vec postovano ali vredi da bude u ovoj temi jer ovo je verovatno jedan od najvecih potresa/preokreta u industriji u poslednjih ko zna koliko godina:

When launching a game using EAC Linux v2 for the first time, players will be prompted to install an anti-cheat systemd service which runs only while a protected game is running. For games that already have the existing EAC Linux support activated, developers will be able to choose whether they want to continue using the older anti-cheat implementation for maximum compatibility or switch to EAC Linux v2 for better cheat protection.
Let’s go through the system requirements for EAC Linux v2 one by one. We expect to iterate on these requirements over time, and we appreciate feedback from developers and distribution maintainers to help refine them.
1. Signed Kernel & Kernel Modules
A custom kernel can easily be modified to bypass integrity checks and return false data to anti-cheat. That’s why we require that the kernel binary in use during anti-cheat protected gameplay is signed with a well-known key.
Unlike Windows, most Linux device drivers are part of the kernel source code directly (in-tree) and will be compiled and signed by your distribution alongside the kernel. There are some exceptions that are maintained separately from the kernel (out-of-tree), notably NVIDIA GPU drivers. If you need to load kernel modules, we require that they meet the same requirements as the kernel—being built by an organization and signed with a well-known key.
2. TPM 2.0
The TPM is a hardware feature that provides security primitives like extend-only Platform Configuration Registers (PCRs) which enable a tamper-resistant boot log to be produced and verified. During boot, each piece of the boot sequence (firmware, boot manager, Linux kernel) can record metadata about the code that will run next and update the extend-only registers. This is extremely valuable, because when properly used, it enables an application like anti-cheat to know what code ran at boot without running at boot itself.
TPM 2.0 is standard on modern consumer hardware, and software support is built into the Linux kernel. We require that systems have TPM 2.0 support and that it is enabled in the BIOS.
3. Secure Boot
Secure Boot authenticates the boot chain. Firmware will only execute a boot manager that verifies against a key in its UEFI key database, and the boot manager is expected to validate the signature of the kernel it loads. This prevents EFI-based cheats or others that run during the boot chain. We require that Secure Boot is enabled in the BIOS and only well-known keys are used to boot.
4. Measured Boot
Measured boot is the process of actually recording metadata about the system configuration and code that will run next, then updating the extend-only registers accordingly. Linux boot managers like systemd-boot and GRUB typically perform these measurements automatically by default. Other boot managers may not support them at all or only perform them if a special configuration is applied. We require these measurements to be present.
5. Input-Output Memory Management Unit (IOMMU)
IOMMU is a hardware technology that controls access between DMA-capable hardware devices and physical memory. When fully activated, it prevents hardware cards designed for cheating from accessing a protected game process. For non-handheld devices, we require that IOMMU is enabled in your system's BIOS and the Linux kernel is configured with IOMMU enabled and passthrough disabled.
6. Kernel Lockdown Integrity Mode
Kernel lockdown is a built-in security feature designed to prevent root from tampering with the kernel. In integrity mode, it blocks root from performing many operations that could be abused for cheating or bypassing integrity checks, like loading unsigned kernel modules, writing to physical memory, or writing to CPU MSRs. We require that lockdown integrity mode is explicitly enabled at boot time.
7. Kexec Disabled
Kexec is a Linux kernel feature that loads a new kernel into a running system without a full reboot cycle. Because parts of the normal boot flow are skipped, measured boot outputs no longer reflect the running kernel or its configuration. This could be abused to load a modified kernel—or change kernel options—to enable cheating without leaving traces in the measured boot log. We require that kexec is explicitly disabled at boot time.
8. Linux Security Module BPF
The LSM BPF feature enables eBPF programs to use Linux Security Module hooks for granular access control and monitoring. This enables anti-cheat to restrict other processes from reading or writing protected game process memory without needing a kernel module, as well as monitor for cheats loaded in different ways. We require the BPF LSM to be loaded and active.
What keys are considered well-known?
Here is a current list of keys that are considered well-known for use as Secure Boot signature database (db) keys and Machine Owner Keys (MOKs), which we plan to expand over time:
- Canonical Ltd. Master Certificate Authority - used by Ubuntu and derived distros like Linux Mint
- Fedora Secure Boot CA - used by Fedora and derived distros like Silverblue
- Universal Blue - used by Bazzite, Bluefin, Aurora, and derived distros
- Debian Secure Boot CA - used by Debian and derived distros
- openSUSE Secure Boot CA - used by openSUSE and derived distros
- SUSE Linux Enterprise Secure Boot CA
- Rocky Linux Secure Boot Root CA
- Microsoft UEFI CA - used to sign non-Microsoft components like the Linux bootloader shim project
- AlmaLinux Secure Boot CA
Can I generate and enroll my own Secure Boot keys to use with other boot options?
Yes, EAC Linux v2’s well-known key requirement only applies to the keys used to verify the boot chain and kernel modules for the boot session where a protected game runs. This means you can easily toggle between an anti-cheat compatible boot path for playing protected games and one that you control yourself using your own keys for any other situation.
Note: If you boot via shim and want to use custom keys for other boot options, enroll them in the Secure Boot signature database (db) instead of enrolling them as Machine Owner Keys (MOKs). Because all enrolled MOKs are typically trusted for kernel module signature verification regardless of whether they were used in the boot chain or not, EAC Linux v2 requires that they are all well-known.
What about Steam Deck?
The Steam Deck does not support the required features for our EAC v2 solution, but we are actively talking with Valve and hope to support it in the future.
Will my account be banned for cheating if I accidentally start a protected game without meeting these requirements?
No, you will just see an error message.
Follow along with the video below to see how to install our site as a web app on your home screen.
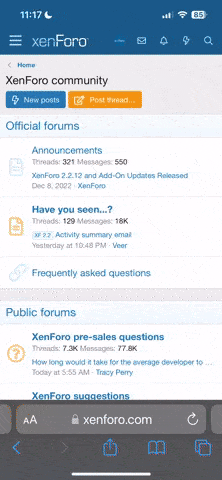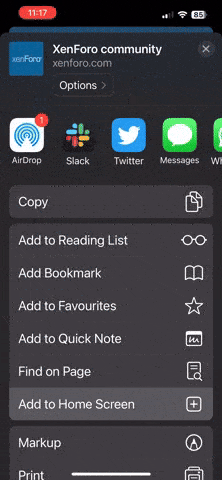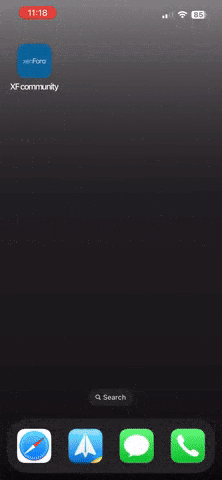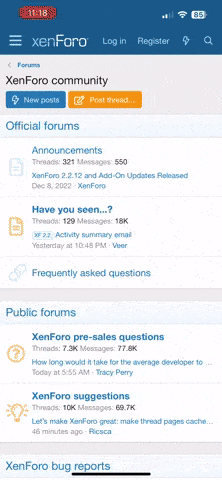
Napomena: this_feature_currently_requires_accessing_site_using_safari